Threat Detection, Investigation and Response (TDIR)
Quickly and efficiently identify, assess and respond to all threats, with Red Piranha
With too many alerts and disparate systems to manage, poor tool implementation and the lack of resources,
it's tough for organisations to implement effective Threat Detection, Investigation and Response.
Up to 10x Increased Visibility - Gain critical visibility and insight into network operations to deal with APTs and previously unknown attacks through network behavioural analytics.
Deploy fully Operationalised and Contextualised Threat Intelligence efficiently and receive Automated Actionable Intelligence to Protect, Detect and Respond to threats proactively.
24/7 access to our “village” of security professionals leveraging Human-machine teaming for improved alert prioritisation and incident response.
Flexible In-line Deployment to avoid disruptive infrastructure changes and eliminate the need for engineering overheads.
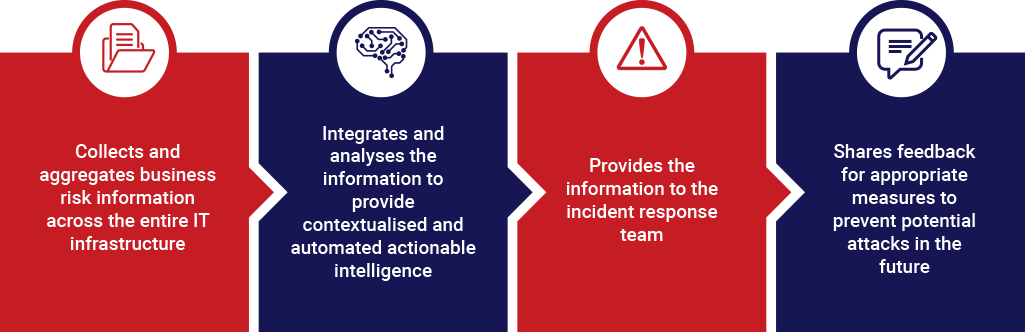
How Threat Detection, Investigation and Response helps your organisation?
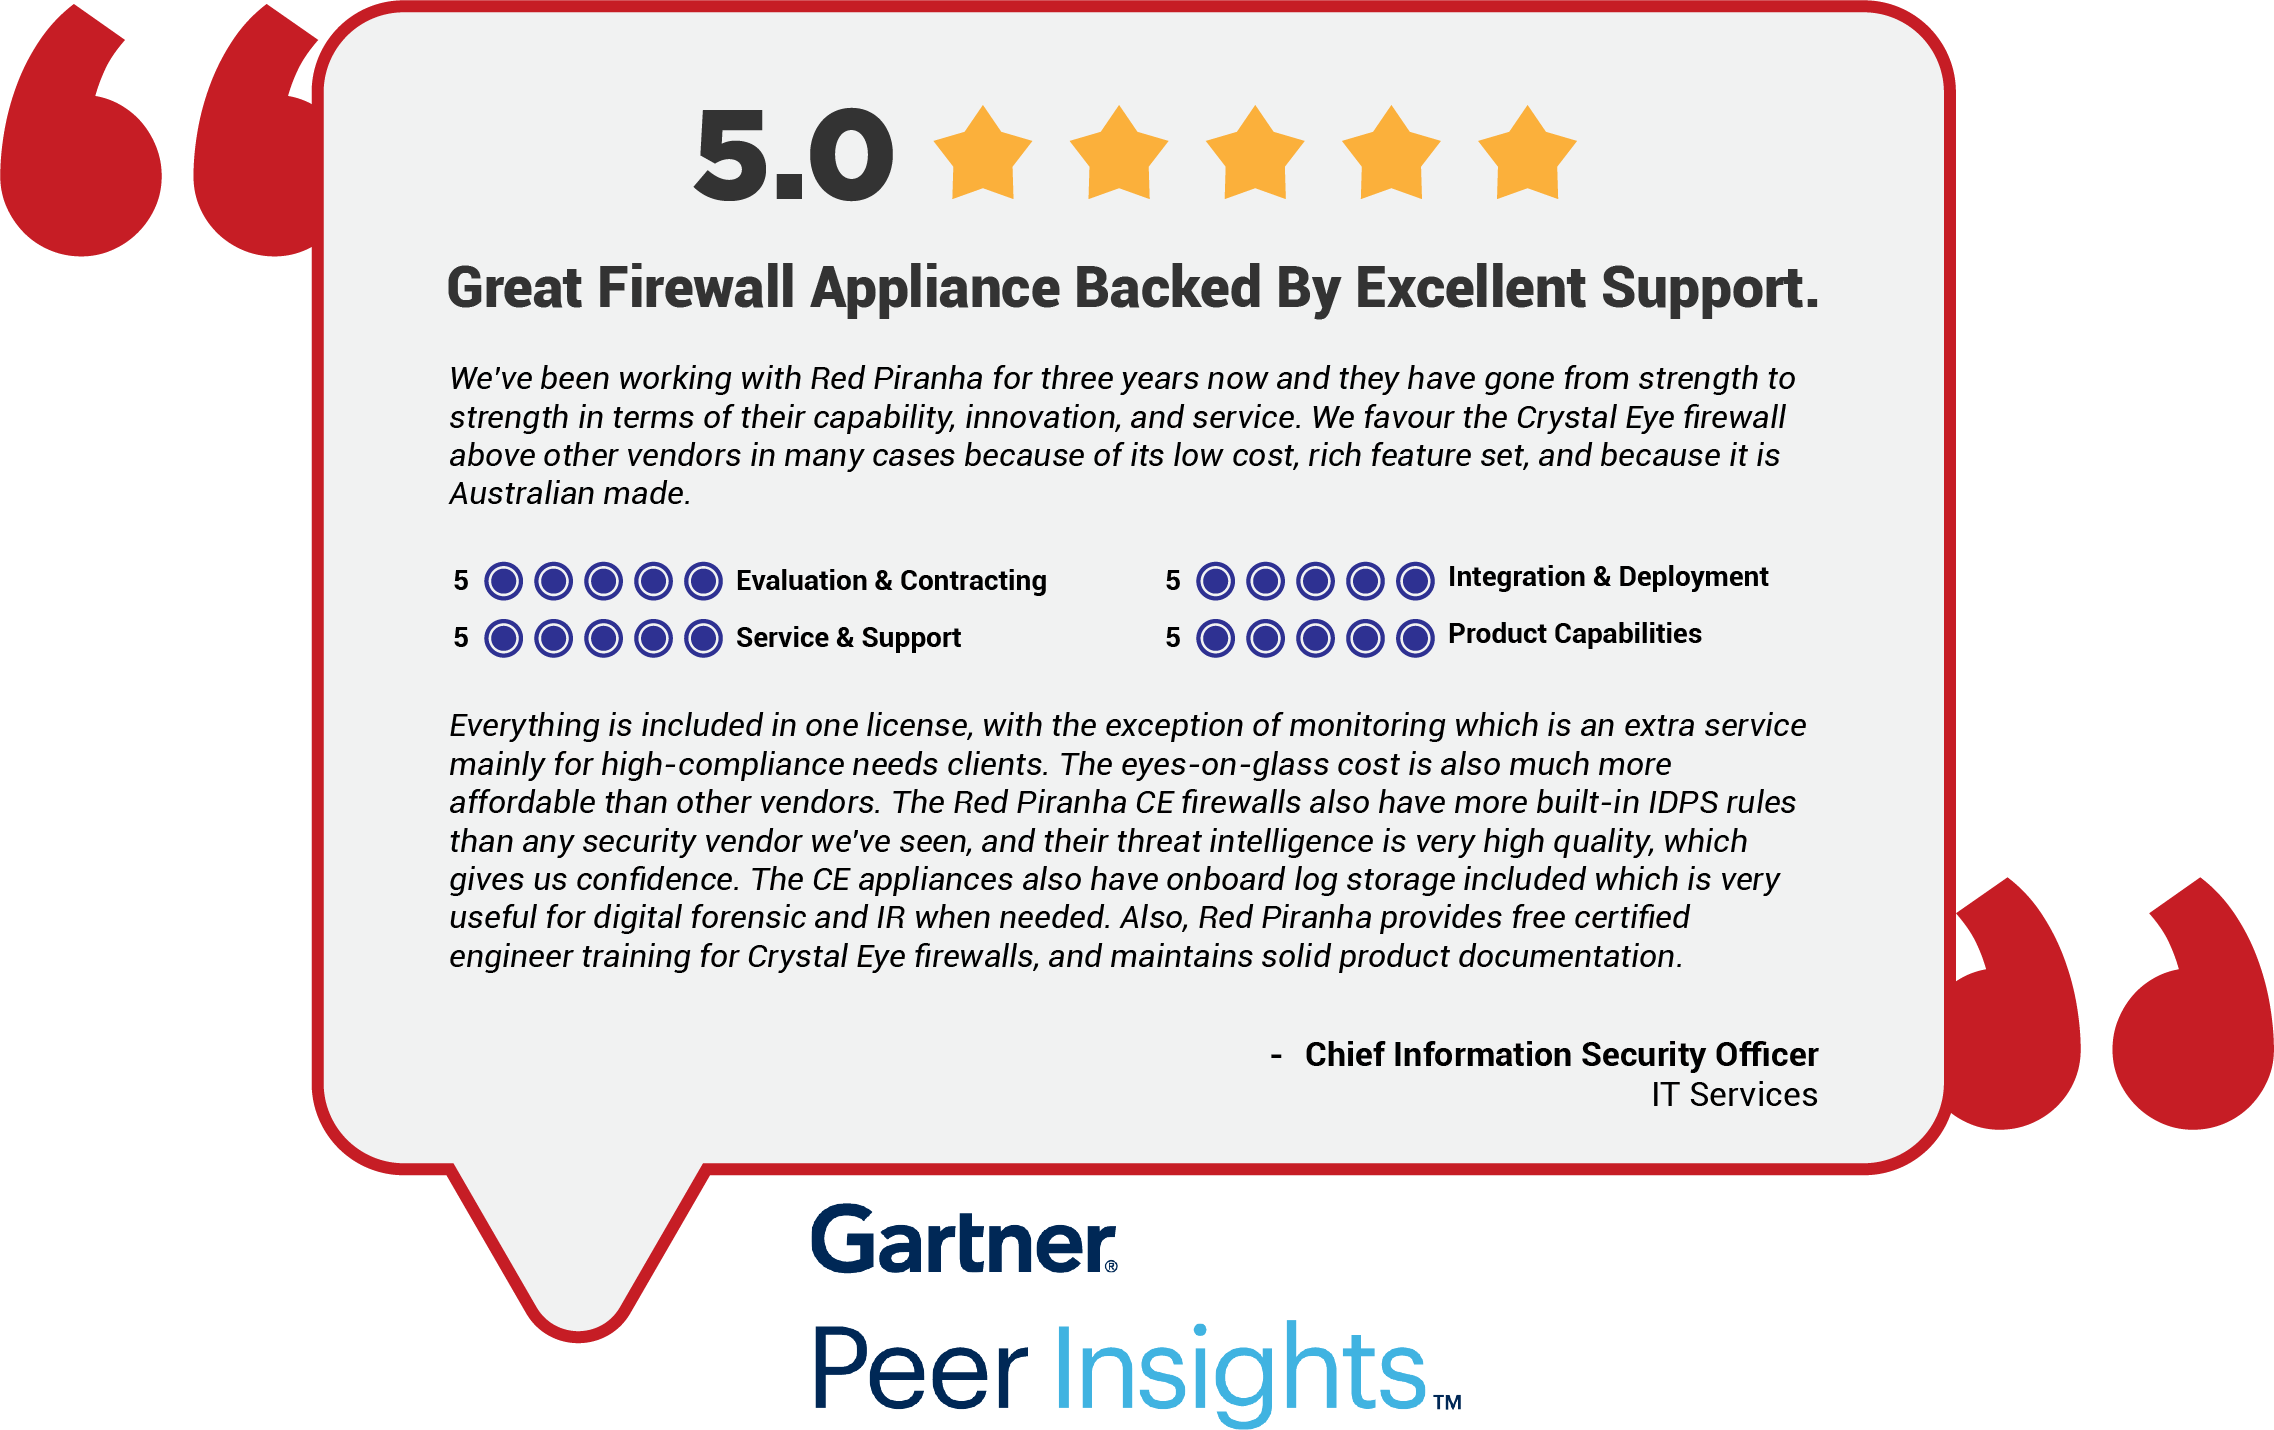
Why Red Piranha's Threat Detection, Investigation and Response Program?
- Advanced heuristics and ML anomaly detection with World-Class Threat Intelligence for contextualised, high confidence alerts.
- Push-button escalation to Red Piranha’s SOC - Remove complexity, instantly escalate an event to the SOC team and enhance security operations.
- Receive instant alerts and after-action reports directly from the Red Piranha SOC team with Platinum SIEM.
- Proactive threat hunting and investigation to detect advanced APTs, LotL (Living off the Land) and other indicators to reduce dwell time.
- Multi-tenanted, single platform sensor deployment to improve detection engineering efficacy across East-West traffic flows.
- Industry-leading forensic log retention for 18+ months to help meet compliance.

Threat Hunt Dashboard
With best-in-class Threat Detection Investigation and Response, effectively detect, correlate and respond to adversary activity on your networks including advanced lateral movement and other IOCs that are often left undetected.
Together with human-machine teaming and state-of-the-art technology, our clients get cohesive protection against advanced persistent threats (APTs) without the need for new specialist engineering teams, reducing the total cost of ownership for maximum security outcomes.
Red Piranha is Australia’s leading developer, manufacturer, and official member of Team Defence Australia for advanced cybersecurity solutions.
24x7x365 protection for your organisation.
Meet your compliance challenges.
Enhance Security Operations
Detect Malware families and CnC call outs
Thwart Sophisticated Attacks
Reduce Total Cost of Ownership (TCO)
We are a proud member of the Cyber Threat Alliance (CTA)

Threat Detection
Threat detection involves identifying potential threats and is primarily done by the SecOps teams. This typically includes collating and sending information to a centralised log management system, commonly known asSecurity Information and Event Management (SIEM)and analysing it for irregularities.

Investigation
Investigation is the process of analysing and evaluating the alerts generated during the threat detection phase to determine the nature and scope of the threat. This includes filtering false positives, identifying the root cause of the infection, assessing the potential impact and determining the appropriate course of action, leading to increased actionability.

Response
Response involves taking action to contain, eradicate, and recover from the incident and prevent future incidents. This includes isolating affected systems, removing malware, patching vulnerabilities and implementing security controls to prevent future attacks.